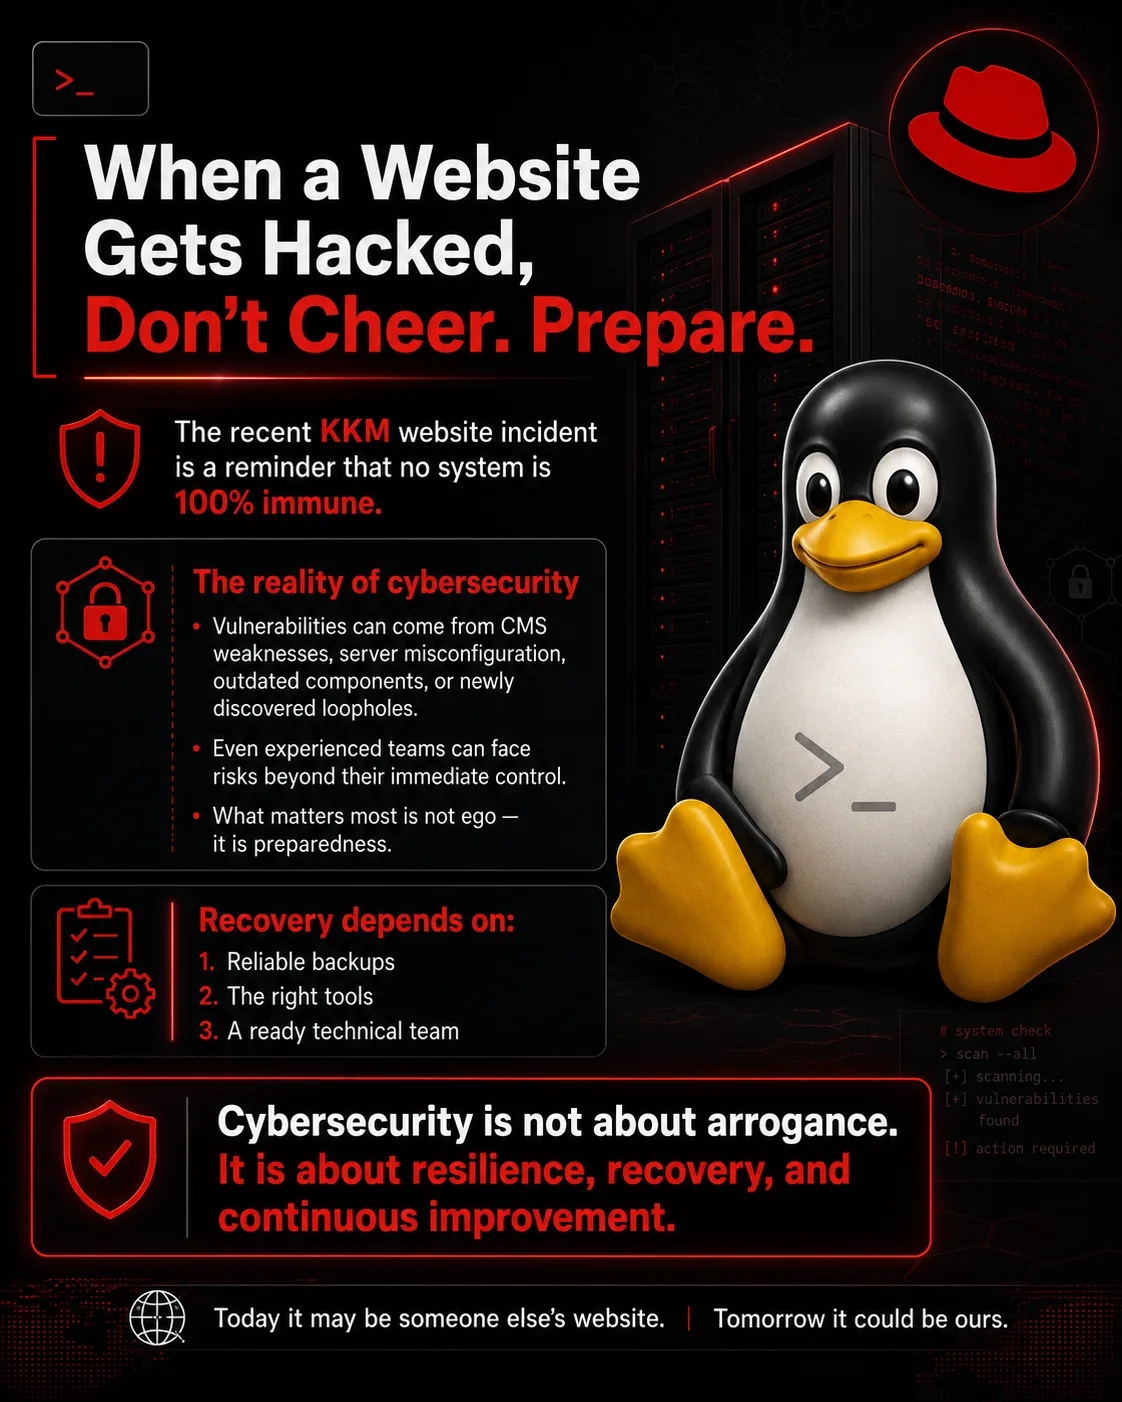
Recent reports about the KKM website being hacked or defaced should remind all of us of one important truth: cybersecurity is not a place for arrogance.
Every time a major website is compromised, many people are quick to criticize. Cybersecurity experts, AI experts, and technical commentators often speak as if their own systems are completely immune to the same risks.
The reality is different.
No website is 100% safe. Government portals, corporate websites, SME websites, CMS-based platforms, and even well-maintained servers can still be exposed to risk. The causes can vary - outdated CMS versions, vulnerable plugins, server misconfiguration, weak access control, poor patch management, or even newly discovered loopholes that were unknown before.
Sometimes, the issue is not simply about whether a team is competent. It is about how prepared the organization is when something goes wrong.
This is where backup, monitoring, regular security audits, server hardening, incident response planning, and recovery procedures become critical.
A hacked or defaced website is not only a technical problem. It is also a business continuity issue, a trust issue, and a reputation issue.
The recovery time depends heavily on three things:
- The quality of the backup
- The tools available
- The readiness of the technical team
Cybersecurity should not be about mocking others when an incident happens. It should be about learning, improving, and strengthening our own systems before we face the same situation.
Today, it may be someone else’s website.
Tomorrow, it could be ours.
Cybersecurity is not about being the loudest expert in the room. It is about being prepared, disciplined, and continuously improving.
#CyberSecurity #WebsiteSecurity #BusinessContinuity #DigitalRisk #IncidentResponse #SME #Technology #NeuralOps

Ruang pembaca
Apa pendapat anda?
Komen disemak sebelum diterbitkan. Email diperlukan untuk moderasi dan tidak dipaparkan kepada pembaca.
เห็นด้วยเรื่องบทความนี้ และทิศทางชัดเจน
Sent this to two people already. Recent reports about the KKM is why.
The direction on poor patch management is exactly right.
First piece I have read that treats every time a major website honestly.